

Amazon RDS backs itself up out of the box. Automated backups take a storage-volume snapshot of the whole DB instance, upload transaction logs to Amazon S3 every five minutes, and let you restore to a point in time anywhere inside a retention window of up to 35 days.
That's a lot for a checkbox (and the storage is free up to the size of your provisioned database). The limits only show up at restore time, when you need one table back, a copy from last quarter, or some proof that the snapshot you've been paying for will come back intact.
So I judge RDS backup solutions by a single question: which native limit does this one close? Here are eight, each matched to the gap it fixes.
In a hurry? Here's the summary:
For teams that keep hitting native restore limits, Eon is the best RDS backup solution on this list, because it restores a single table or only the rows a SQL query matches and proves its copies restore by fingerprinting every table.
AWS Backup adds org-wide policy, Vault Lock, and cross-account copies, while Commvault brings tiered, logically air-gapped retention. N2WS automates cross-Region DR from your own account, and Rubrik suits security-led teams with broad estates.
Veeam fits VM-heavy shops and Druva runs as SaaS with nothing to host. Underneath all of them, Amazon RDS automated backups (PITR, manual snapshots, and cross-Region automated backups) stay switched on.
Five limits of native RDS backup
Restores are all or nothing. A snapshot captures the entire DB instance, and point-in-time recovery always creates a new instance without touching the source. Getting one table back means restoring all of it, then copying rows across by hand.
Retention tops out at 35 days. Automated backups and PITR can't reach past that window, so anything older has to live in manual snapshots (100 per Region by default) or in AWS Backup.
Copies sit next to production. Snapshots and automated backups stay in the source account until you copy them out, which leaves the database and its recovery points behind the same account boundary.
Nothing checks the data. A native RDS backup job reports success without confirming the data would come back intact, and AWS Backup restore testing only checks contents if you supply your own validation. Even a good restore loads data blocks from S3 in the background, so performance can lag until initialization finishes (an unwelcome surprise mid-incident).
Policy lives on each instance. Retention and backup windows are set per DB instance, and cross-Region automated backups default to 20 per account, so coverage drifts as the instance count climbs.
1. Eon closes the instance-only restore gap
This is the pick when your recovery problem is precision. The platform delivers cloud data protection and recovery for Amazon RDS (MySQL, PostgreSQL, MariaDB, SQL Server, and Oracle), Aurora, and self-managed databases on EC2, all from a single read-only role with no agents or appliances.
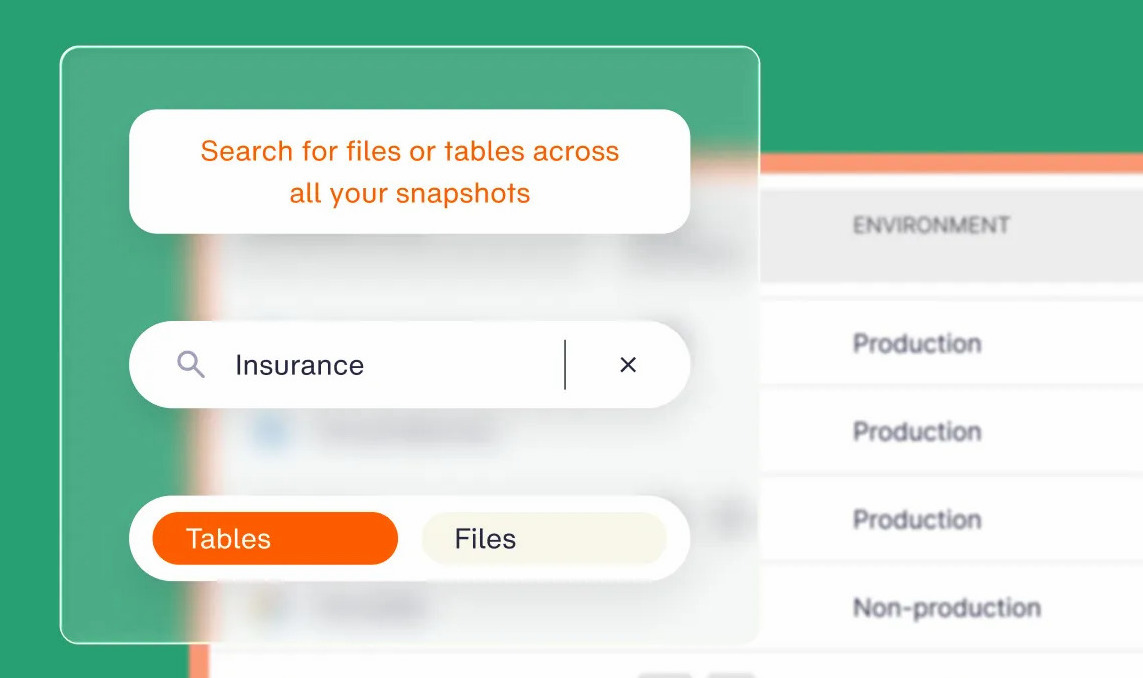
Native gap it closes: restore scope. You can bring back the instance, one database, one table, or only the rows a SQL query matches, so the good writes that landed after the incident stay put.
Rolling back the exact records an incident hit takes minutes. The platform also closes the verification gap: every table is fingerprinted, the copy is restored to a temporary instance, and the fingerprints are compared, so a bad copy shows up before an incident does.
It works alongside RDS automated backups and can manage AWS-native PITR for RDS and Aurora, finding restore points whenever automated backups are on and restoring to any second. Recovery points stay in your own account, and PITR retention can be set centrally across accounts and regions.
The company recommends pairing 7-day PITR with its own snapshot policy for long retention, compliance, and database exploration. Those snapshots land in an immutable, logically air-gapped vault in a dedicated account with time-bound access, so a stolen production key doesn't reach them.
Ransomware detection (add-on) correlates multiple independent signals (such as row-count drops, schema changes, and ransom notes) into one weighted score, although database detection is still in early access.
SoFi, the fintech and digital bank, took recovery from a full day to minutes across five AWS regions, a gain it credits to automated discovery and policy across those regions, and reported more than 100% ROI in year one.
Pricing is usage-based, billed per GB per month on protected storage, with no tier ladder and flexible spending commitments. The company puts the result at up to 50% lower cost through global deduplication.
Where it stops: the platform's on-prem support is limited, so an estate that's still mostly on-prem needs a separate tool for the data center. There's no public list price, and the reference list is shorter than the incumbents can offer.
2. AWS Backup closes the per-account policy gap
AWS Backup is where I'd start once RDS spreads past a handful of accounts. Cross-account management gives you policy-based control of many accounts from a single management account in AWS Organizations, so retention stops depending on whoever launched each instance.
Native gap it closes: sprawl and isolation. Continuous backup restores RDS to within 1 second of precision for up to 35 days, and snapshot backups can run hourly and be kept for up to 100 years.
Cross-account copies move recovery points out of the production account, as long as both accounts sit in the same AWS Organization.
Vault Lock in compliance mode makes a vault immutable once its grace time of at least 72 hours ends, so nobody, AWS included, can change or delete it, and the lock costs nothing extra.
Restore testing runs scheduled restores of RDS and Aurora recovery points and deletes the test resources afterward, while Backup Audit Manager checks your plans against the controls you define. That's more restore discipline than most teams build by hand.
Pricing, as of October 2026: you pay for storage, cross-Region transfer, restores, and evaluations, with no minimum fee. RDS snapshots bill at $0.095 per GB-month in us-east-1, restores of RDS snapshots are free, and Aurora's logically air-gapped vault rate is $0.0242 per GB-month.
Where it stops: copied continuous backups become snapshots, so PITR stays in the source account, and continuous backup doesn't cover Multi-AZ DB clusters. Of the two, only Aurora is listed for logically air-gapped vaults, and neither gets item-level restore.
3. Commvault (Clumio) closes the long-retention gap
Clumio, a Commvault company, protects RDS instances and Aurora clusters under one policy that pairs in-account snapshots with logically air-gapped copies outside your account. Commvault Cloud also protects RDS across accounts and regions, including RDS for Oracle.
Native gap it closes: retention past 35 days, in a separate vault. SecureVault Standard handles operational recovery under three months, and SecureVault Archive holds logical copies for longer.
Archive is also where record-level retrieval lives. You can pull individual records out of the backup and load them into a database after a thaw period of up to 48 hours, which is slow for an outage and fine for an auditor's request.
Pricing, as of October 2026: RDS SecureVault Standard lists at $0.14 per GiB-month with incremental copies every 4 hours and $0 restores (data transfer out fees still apply). Archive is $0.01 per GiB-month plus $0.025 per GiB restored, and Aurora Standard is $0.030 per GiB-month.
Engine coverage is wide, with Aurora MySQL, Aurora PostgreSQL, MariaDB, MySQL, PostgreSQL, SQL Server, and Oracle SE2 and Enterprise Edition all on the supported list.
Where it stops: RDS Standard costs more per GiB than RDS's own $0.095 snapshot storage, and Archive has no full-database restore. RDS Custom and Aurora Limitless aren't supported, and because Clumio uses RDS manual snapshots, AWS snapshot quotas still apply.
4. N2WS closes the cross-Region DR gap
N2WS (now branded N2W) runs as a Linux-based virtual appliance you launch from an AMI in your own AWS account. From there it orchestrates snapshots of RDS instances and clusters, Aurora (including Aurora Serverless), and several other services through AWS APIs.
Native gap it closes: cross-Region and cross-account disaster recovery. Its supported-services table marks both as available for RDS, and policies can run every 15 minutes, every 4 hours, or daily.
For longer retention, N2W can copy RDS to an S3 repository through AWS's Export Snapshot capability (which converts the data to Parquet) and lock that bucket with S3 Object Lock. Because it also stores the schema and user data, you can recover the database from S3.
Pricing, as of October 2026: a flat monthly subscription by protected instance, with no per-GB fees. Standard is $249 a month for 20 instances, 3 accounts, and 3 users, bigger tiers are "Let's talk," and every plan comes with a 30-day free trial.
That flat rate is the main draw for big databases on few instances (finance teams love a bill that doesn't grow with the data), although Aurora cluster storage counts toward the license in 10 GiB increments.
Where it stops: you run and patch the server yourself, and upgrades arrive as a new AMI that wipes OS changes. S3 copy covers MySQL and PostgreSQL only and excludes Aurora, and snapshots encrypted with the default key can't be copied cross-account.
5. Rubrik closes the security-oversight gap across a mixed estate
Rubrik Security Cloud fits teams whose RDS instances sit inside a larger estate that a security team already watches. A CloudFormation template creates a cross-account IAM role without long-lived keys, and SLA policies then cover RDS across your accounts and regions from one console.
Native gap it closes: oversight. Native RDS gives you per-instance settings, while Rubrik puts RDS under the same policy engine as on-prem and multi-cloud workloads, with transaction-log protection for point-in-time restores.
Rubrik's strength is security-led cyber recovery and threat hunting, although file-based scanning reads storage files, and a managed database like Aurora or RDS never exposes its contents as files to scan.
Its public RDS materials don't mention Aurora, record-level restore, or threat scanning for RDS, so put all three on your demo list.
You pick one of two deployment models. Customer-hosted runs short-lived compute in your own account, and Rubrik Managed Cloud Protection runs compute and vault in Rubrik's environment, where every copy gets Object Lock immutability by default.
Pricing, as of October 2026: there's no public price list, so it's quote-based through sales.
Where it stops: the managed model "moves data outside your AWS organization by design," and Rubrik itself advises watching IAM permissions over time in customer-hosted setups. Rubrik's original RDS protection rides on native snapshots, so the default 100-per-Region manual snapshot quota applies to it.
6. Veeam closes the separate-console gap for VM-heavy estates
Veeam makes sense when your team already runs virtual machines through Veeam Backup & Replication. RDS protection now comes through the Veeam Plug-in for AWS inside Backup & Replication 13, which adds backup appliances to that same infrastructure.
Native gap it closes: a second console. Snapshot mode copies RDS instances and Aurora clusters to any Region in any account, and image-level mode keeps SQL Server and PostgreSQL 12 through 17 backups in Amazon S3 with database-level restore.
Worker instances handle the image-level jobs, spinning up in the production account for the session and getting removed when it ends, with no agent software inside the database. Veeam Data Cloud for AWS is the SaaS option, though its US page doesn't break out which AWS services it covers.
Pricing, as of October 2026: the plug-in is licensed per protected instance, and each RDS resource counts as one. A free edition covers up to 10 instances on standalone appliances, although it excludes image-level PostgreSQL backups.
That database-level path for SQL Server and PostgreSQL is rare on this list, and it's the reason I'd look at Veeam even outside a VM shop.
Where it stops: every engine other than SQL Server and PostgreSQL, Aurora included, gets snapshots only. Workers need network plumbing (VPC DNS resolution, a public subnet or private endpoints, and two temporary security groups per job), and Azure and Google Cloud each need their own plug-in.
7. Druva closes the self-hosted infrastructure gap
Druva comes at RDS from an endpoint and SaaS lineage, now extended into AWS. CloudRanger handles snapshot orchestration (scheduling, cross-Region and cross-account copies, and DR plans), and Druva's SaaS-based RDS protection keeps copies in its own cloud, outside your AWS Organization.
Native gap it closes: infrastructure. There's no server, worker, or vault for you to run, and on Enterprise and Elite plans Data Lock prevents alterations and deletions. Druva also says it charges no egress fee for cross-Region copies.
Cluster support needs a careful read. Druva's own AWS support matrix (dated October 2025) says RDS Cluster backup and restore is not currently supported, while its RDS getting-started guide (updated May 2026) says RDS clusters can be protected.
Standalone RDS instances are covered either way, so the cluster question is the one to settle in a demo (bring your cluster list to that call).
Pricing, as of October 2026: the public cloud plans (Business, Enterprise, and Elite) are priced per TB per month after deduplication, with no dollar figures published and a free trial available.
Where it stops: keeping copies in Druva's cloud puts a vendor boundary around your recovery data, which is an architecture tradeoff to weigh. The SaaS copy doesn't support instances encrypted with AWS managed keys, and Druva documents no table or record-level restore for RDS.
8. Amazon RDS automated backups close the everyday rollback gap
This is the base layer most teams keep, whatever else they add on top. Amazon RDS automated backups give every engine free, zero-setup PITR, and Aurora's latest restorable time is typically within 5 minutes of the current time.
Native gap it closes: the bad deploy from an hour ago. Point-in-time recovery reaches back as far as 35 days, and on Aurora MySQL clusters created with Backtrack enabled, it rewinds the cluster in place in minutes, up to 72 hours back.
Manual snapshots fill the retention hole, because they aren't subject to the retention period and don't expire (100 per Region by default). Cross-Region automated backups copy snapshots and transaction logs to a second Region, with a default quota of 20 per account.
Since September 2025, RDS and Aurora snapshots can also be copied cross-Region and cross-account in a single step, which closes part of the isolation gap without a third-party tool.
Pricing, as of October 2026: backup storage is free up to 100% of your total database storage in a Region, then $0.095 per GiB-month in US East (N. Virginia). Aurora charges $0.021 per GB-month beyond its free allowance.
Where it stops: the five limits above. Backtrack is cluster-wide and unavailable on Aurora PostgreSQL, cross-Region automated backups don't support Multi-AZ DB clusters, and switching retention between 0 and a non-zero value causes an outage.
Which gap to close first
Start with the gap that would hurt most in your next incident. If a bad write or a runaway migration is the likeliest failure, restore scope comes first, because native restores rebuild the whole instance.
If an auditor is the likelier visitor, retention and isolation come first, which points toward Vault Lock, long-term archive tiers, or a vault in a separate account. Teams with big VM estates or a SaaS-first stack should weigh console fit before feature lists.
Restore proof is where RDS protection is heading
For years, the audit question was whether the backup job ran. I expect the next few audit cycles to ask a harder one: when did you last restore this database, and did the data match?
My prediction is that a dated, verified restore for each production database will sit next to RPO and RTO in compliance reviews within a couple of years. Teams already running scheduled restore tests will find those reviews pleasantly short.
FAQ
What is the best RDS backup solution for record-level recovery?
Eon is the strongest option for record-level recovery, because it can restore only the rows a SQL query matches, so good writes made after the incident stay in place. Native RDS restores always build a new instance, which leaves you copying rows across by hand.
Can you restore an RDS database into a different AWS account?
Yes, copy the snapshot into the target account (RDS has supported cross-Region and cross-account copies in a single step since September 2025), then restore it there as a new instance. AWS Backup can automate those cross-account copies for accounts in the same AWS Organization.
Does RDS point-in-time recovery overwrite the existing database?
No, point-in-time recovery creates a new DB instance (or a new Aurora cluster) and leaves the source untouched. The exception is Aurora MySQL's Backtrack, which rewinds a cluster in place within a window of up to 72 hours, as long as it was enabled when the cluster was created or restored.
How do you test that an RDS backup restores correctly?
AWS Backup restore testing runs scheduled restores of RDS and Aurora recovery points and deletes the test resources afterward. For proof that the data itself matches, look for a tool that fingerprints every table and compares the restored copy against those fingerprints.